

Cloud security myths: why default settings do not protect you
Read the original in Spanish →
In recent weeks I have had several meetings with managers that have left me really uneasy. There is a systematically repeated pattern that seemed like we should have already overcome.
I sit down with a CEO or managing director to review their digital strategy and, when I bring up the topic of specific investment in cloud security, I receive the same response, almost identical: _«That issue no longer worries us so much. Now we are in the cloud.”
This phrase denotes a false sense of security that is putting the continuity of entire businesses at risk. Migrating infrastructure does not mean externalizing risk; It simply changes the nature of it.
Below, I discuss why this reasoning is false and how to correct it before it’s too late.
1. The misconception: Infrastructure vs. Use
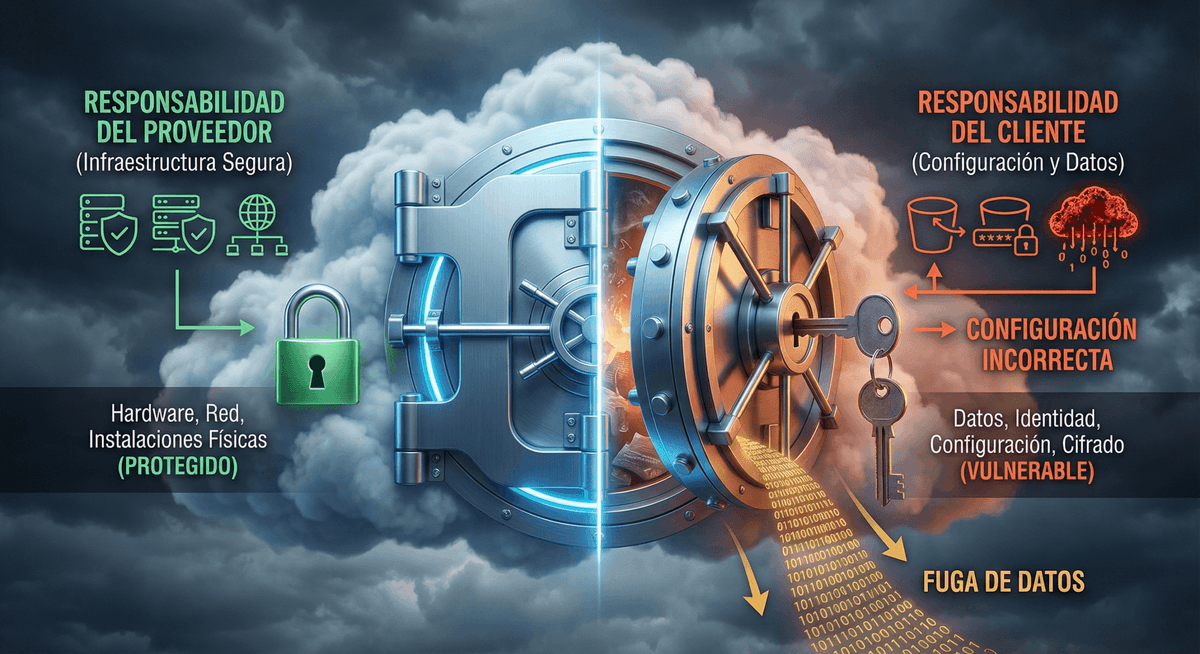
Many managers confuse security of the infrastructure with security in the infrastructure.
Large providers (Amazon, Microsoft, Google) invest billions in protecting their data centers. Its servants are physical and logical fortresses. However, they provide you with a secure environment, not a secure use of it.
The analogy is simple:
- The provider rents you an apartment with the best armored door on the market (the infrastructure).
- If you decide to leave the door open, or give copies of the key to strangers (identity configuration), the theft is your responsibility, not the building owner’s.
2. The contract that no one reads: Shared Responsibility
This is not an opinion, it is a contractual clause. All cloud providers operate under the Shared Responsibility Model.
- The Supplier insures: The hardware, the base software, the global network and the physical facilities.
- You secure: Your data, identity and access management (IAM), encryption, firewall configuration and operating system.
If an attacker breaks in because an employee used a weak password or because you left a database exposed to the Internet, the provider won’t cover you. Your contract was fulfilled: the server did not fail, you failed to configure it.
3. The data: The enemy is in the configuration
Statistical reality contradicts the intuition of being “protected by the giant.” According to projections from consulting firms such as Gartner, up to 99% of security failures in the cloud are the fault of the customer, not the provider.
The current attack vectors do not seek to break Google’s cryptography. They look for basic human errors:
- Storage Buckets set to “public” by mistake.
- Privileged access credentials without multi-factor authentication (MFA).
- Excessive permissions granted to users who do not need them (violation of the principle of Least Privilege).
Tactical Guide: How the CISO can unlock the budget
This is the critical point. I’ve seen competent CISOs lose the budget battle because they try to sell “tech fear” instead of “business risk.”
If you are a security manager and your leadership believes that the cloud is secure by default, use these four arguments to justify investing in cloud security tools (such as CSPM or CWPP):
A. Translate «Visibility» to «Cost Control»
- The problem: In the cloud, it is easy to set up servers and forget them (“Shadow IT”). These forgotten assets are unguarded backdoors.
- The argument: “We need security tools not only to protect ourselves, but to see what we are using. Visibility allows us to eliminate zombie assets and reduce the cloud bill, paying for the security tool with our own savings.”
B. Attack speed
- The problem: In a traditional data center, an attack can take days to propagate. In the cloud, using automated scripts, an attacker can copy your entire database in minutes.
- The argument: «Manual security does not scale in the cloud. We need defensive automation. “We do not pay for ‘more security’, we pay for ‘speed of reaction’ to prevent a minor incident from becoming a notification to the data protection agency.”
C. Regulatory Compliance (GDPR/ISO)
- The problem: The provider complies with their part of the rule, but you are the custodian of your customers’ data.
- The argument: «AWS/Azure complies with ISO 27001, but that does not certify our company. If external auditors see that we do not manage who accesses the data, the fine is for us, not for the provider.
D. The cost of re-engineering
- The problem: Fixing poor security architecture once the application is in production is more expensive than doing so in design.
- The argument: «Investing now in Cloud-Native security is a measure of financial efficiency. “It prevents us from having to stop development in six months to rewrite the platform due to an architectural failure.”
Conclusion
The cloud is a powerful tool, but it is not an autopilot. Believing that we are safe simply by “being in the cloud” is not a strategy; It is negligence.
Review your accountability model today. If you’re not actively managing your cloud security posture, no one is doing it for you.