

What is Continuous Threat Exposure Management (CTEM)?
Read the original in Spanish →
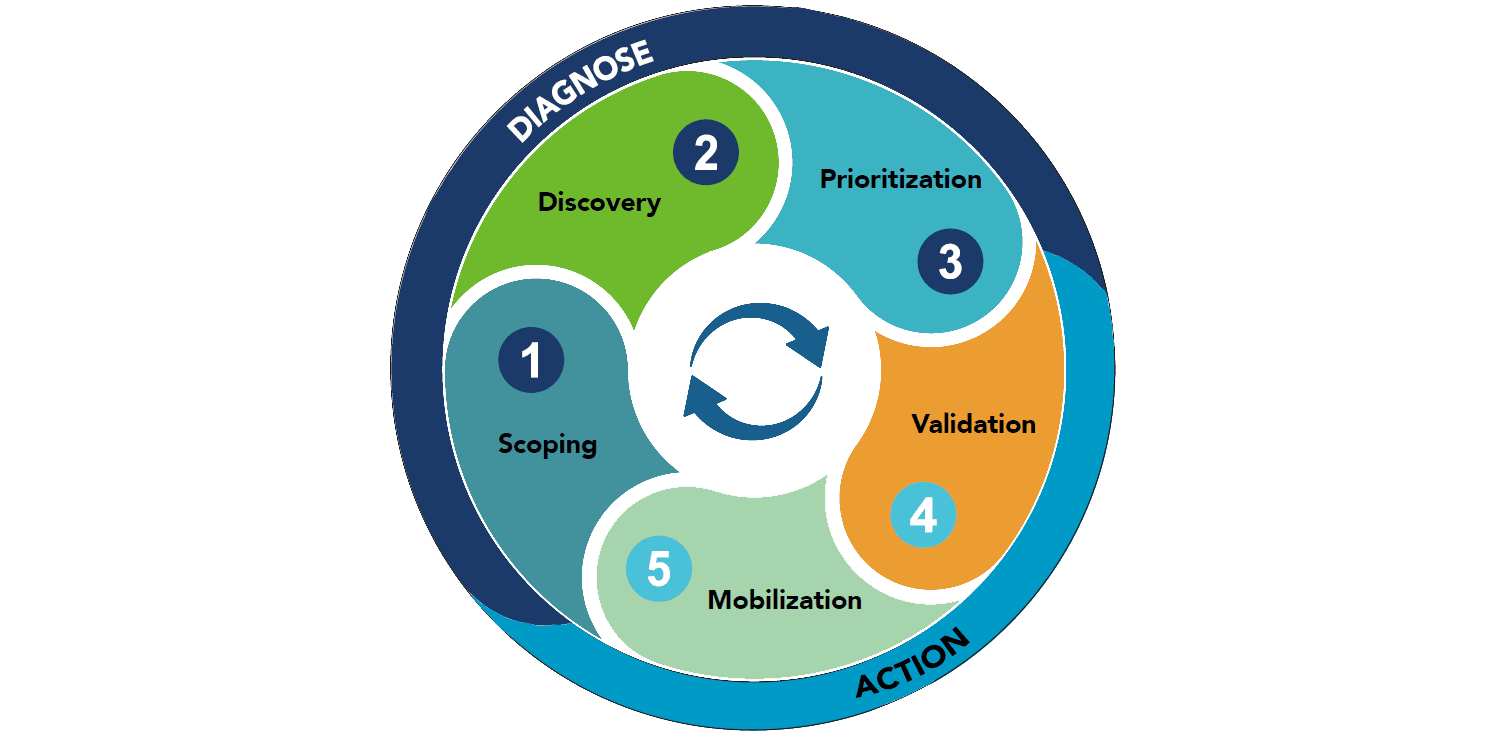
Continuous Threat Exposure Management (CTEM) is a proactive, holistic cybersecurity program designed to continuously identify, assess and reduce an organization’s exposure to threats. It is a five-stage framework that helps organizations identify vulnerabilities and exposures, correlate them with potential attack paths, prioritize them based on their risk to critical assets, and monitor progress as they implement remediation activities.
The five stages of the CTEM program as a continuous process to manage exposure to threats. These stages are:
- Scoping:
This initial stage focuses on understanding an organization’s attack surfaces and the importance of each asset to the business. It involves identifying key attack surfaces and requires the involvement of multiple decision makers, including IT, legal, GRC, development, R&D, product, and business operations team leaders.
It also involves collaboration between business and security functions to define what is critical or high value for the organization’s digital assets.
- Discovery:
At this stage, each asset is evaluated for potential exposures and how these exposures correlate with particular risks is analyzed.
This stage goes beyond individual vulnerabilities as it includes other types of exposures, such as Active Directory, identity, and configuration risks, as well as how exposures can be chained together to create attack paths to assets. It involves mapping infrastructure, network, applications and sensitive data assets to find configuration errors, vulnerabilities and other technical, logical or process defects, and classify their respective risks.
- Prioritization:
Exposures are analyzed to weigh the level of known threat they have posed “in the real world” and the importance of the assets directly affected. This stage is crucial because large organizations often find that there are many more exposures than they can address.
CTEM helps prioritize remediation by making clear which actions are most beneficial in reducing the greatest amount of risk to critical assets. The likelihood of exploitation, with or without taking into account compensating controls, is assessed as a basis for rating its relative importance.
- Validation:
Validation examines how attacks can occur and the probability of their occurrence. Various tools can be used for different uses, including validation for prioritization (as in stage 3), continuous testing of security controls, and automation of periodic penetration tests. Simulated or emulated attacks are launched on previously identified exposures to evaluate the effectiveness of existing defenses and validate that immediate response and remediation are appropriate.
- Mobilization:
This stage ensures that the entire organization understands its role and responsibilities within the program. It is optimized when both the security team and the IT teams involved in the remediation are clear about the risk reduction value of any remediation effort, as well as reporting to show the overall trend of improvements made to the security posture over time.
Key Differences between CTEM and RBVM
Both CTEM and risk-based vulnerability management (RBVM) are cybersecurity strategies designed to help organizations manage risk. However, there are important differences between the two approaches:
- Scope of exhibitions:
- RBVM: It focuses mainly on vulnerability management (CVEs). It relies on tools to assess existing vulnerabilities and determine the amount of risk each poses to critical business assets, based on known “real-world” exploitation of vulnerabilities.
- CTEM: Takes a broader approach, covering not only vulnerabilities (CVEs), but also identity issues and configuration errors. CTEM recognizes that attackers regularly exploit these other types of exposures, and therefore it is crucial to manage them as well.
- Holistic approach vs. limited:
- RBVM: Limits itself to prioritizing individual vulnerabilities, without taking into account how these vulnerabilities could be connected to each other or how an attacker could chain them together to create an attack path.
- CTEM: Takes a holistic view of the environment, analyzing how different exposures can be combined to create attack paths towards critical assets. This broader view allows organizations to better prioritize their remediation efforts and focus on the highest risk areas.
- Prioritization of remediation:
- RBVM: Prioritizes remediation based on the risk posed by each individual vulnerability. This approach can be useful, but it can lead organizations to overlook vulnerabilities that, while individually may appear low risk, can be exploited in combination with others to create a high-risk attack path.
- CTEM: Prioritizes remediation based on actual impact on critical assets. This means that CTEM considers not only the risk of a single vulnerability, but also how that vulnerability could be used in the context of a broader attack path.
- Continuous management vs. punctual:
- RBVM: Often implemented as a one-time or periodic process.
- CTEM: Emphasizes continuous evaluation and improvement. Recognize that IT environments are constantly changing, with new exposures emerging all the time.
Conclusion
CTEM can be considered an evolution of RBVM, addressing the latter’s limitations by broadening the scope of exposures considered, adopting a holistic view of risk, prioritizing remediation based on actual impact, and emphasizing continuous evaluation and improvement.